 E-Magazine
Over 5,000 Cursor users at risk! Fake Claude Code extension can steal your data and let hackers control your PC
Fake Claude extension puts 5,000+ Cursor users at risk.
Malware could steal data and give hackers PC access.
Cursor removed the extension and urged users to secure their devices.
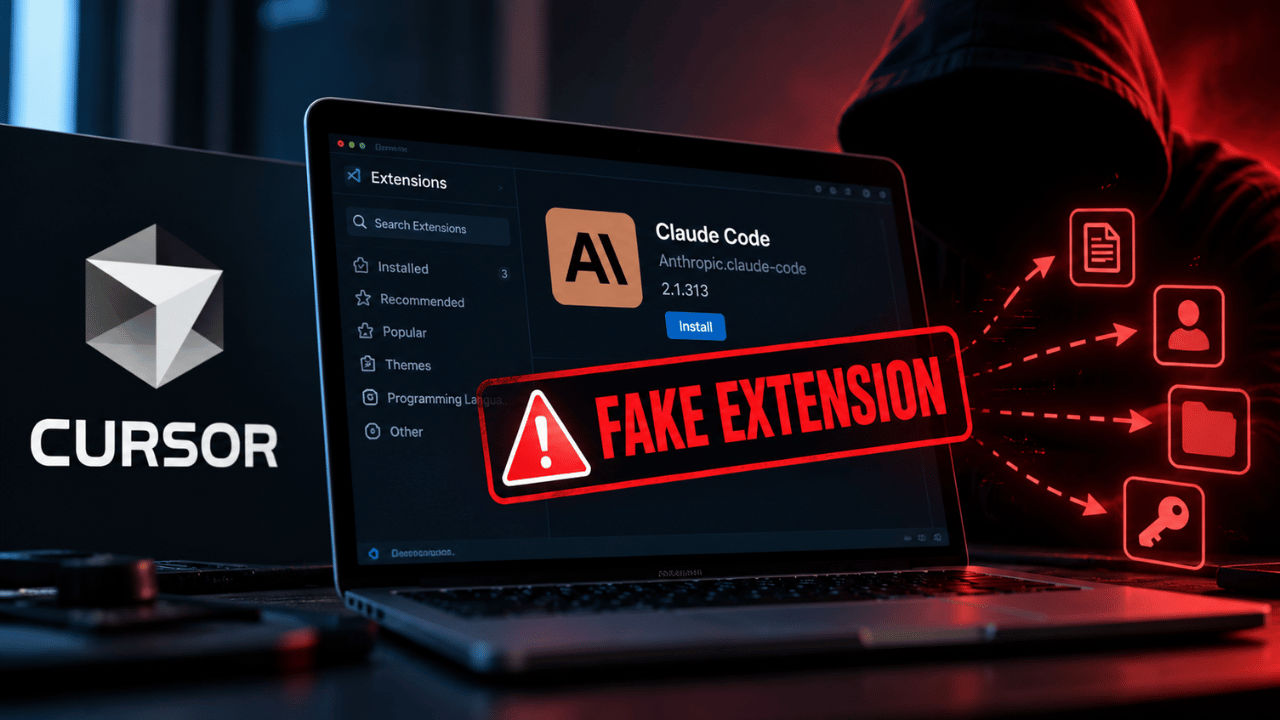
Cursor, an AI-powered software development environment and coding agent has recently warned the users about Anthropic's Claude Code extension. The company added that the malicious version of the extension was not developed by Anthropic but has affected over 5,000 Cursor users. As per the company, the harmful code could collect details about you and try to create a hidden way for attackers to access it remotely. Cursor also confirmed that they have removed the package, shut down the server used in the attack and found no evidence that other extensions were altered. However, they have also directed users to check their devices just so that they can ensure that they are safe.
Cursor security incident: What happened?
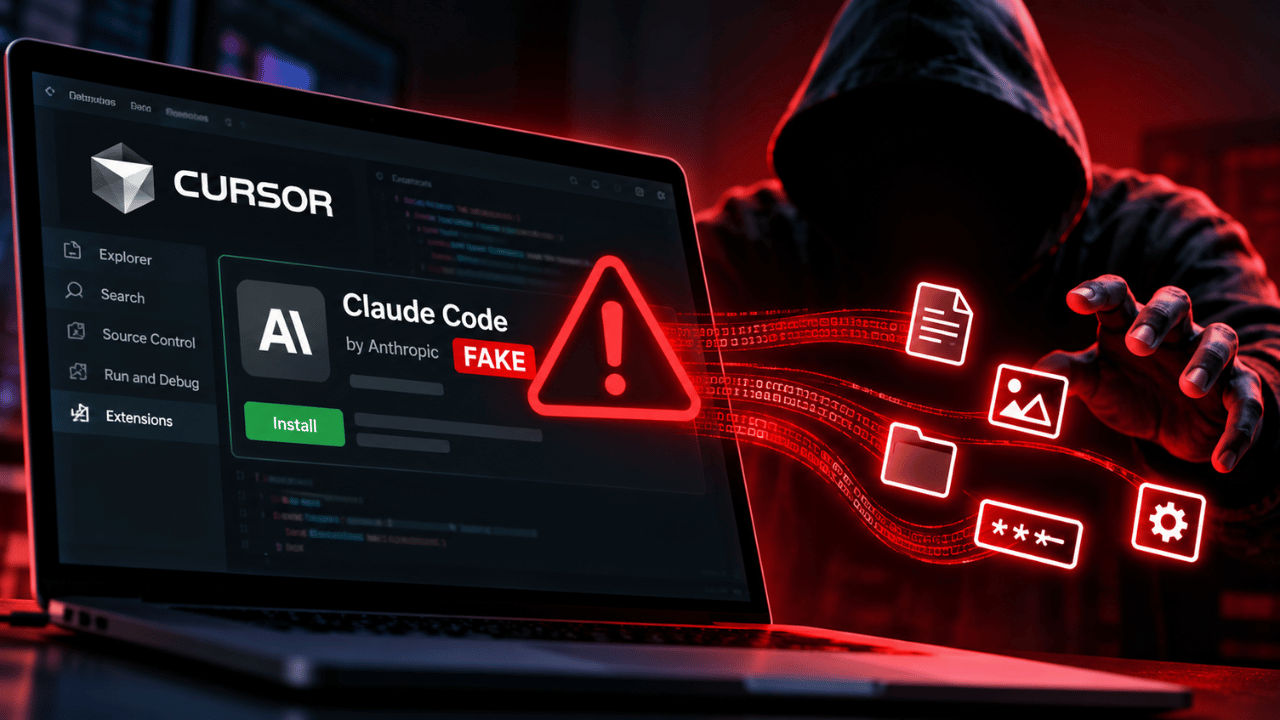
According to a blog post from Cursor, the company has found a fake version of Anthropic’s Claude Code extension on the Cursor VS Code extension marketplace. The malicious extension goes by the name Anthropic.claude-code version 2.1.313 and was available between 2:27 am and 1:35 pm Pacific Time on October 29.
We identified a security incident affecting a modified Claude Code VS Code extension accessed through our Cursor IDE extension marketplace, impacting at most 5,000 users. This malicious version of the extension was not developed by Anthropic. It does not impact other extensions downloaded from the https://t.co/sJRGX5jLXW, Grok Bot, Grok or our other SpaceXSI products. In response, we took down our extension marketplace this afternoon, worked with relevant providers to neutralize the malware, and have reinstated the marketplace after confirming there is no further risk. If affected, please review instructions in this blog post to understand how to find the malicious package and establish a path to mitigate any potential impact. We are asking all customers update to Claude Code for VS Code version 2.1.314: https://t.co/ESqf7YEtHZ
— Cursor (@cursor_ai) October 30, 2026
The blog post also stated that once the extension is installed, it tries to collect information such as the computer's name, username, operating system, working folders, Git email address and public IP address.
What's more concerning that, it also tried to add an unauthorised security key to the computer and create a hidden remote connection which could work as a gateway for the hackers to infiltrate your device. Furthermore, the bugged extension also installed background programmes that could keep trying to establish this connection even after the extension was removed.
Anthropic's involvement
Anthropic is not directly involved in the breach, as Cursor itself has confirmed that the malicious extension was not developed by Anthropic. Moreover, there is currently no evidence that Anthropic has officially distributed the extension or other versions of the extension affected.
Cursor security incident: Are you at risk
The company has confirmed that the users who installed or updated to the Anthropic Claude code version 2.1.313 through Cursor's Extension Marketplace during the affected period are at risk. While the exact number of affected users is still unknown, the company estimates that up to 5,000 users may have been affected. Cursor also confirms that it will contact impacted users directly to ensure that the data is safe.
What should you do?
To ensure that you're safe start by checking your device for an unauthorised SSH key labelled svc-telemetry. Not only that, but Cursor has also provided separate checking and removal instructions for macOS and Windows users.
If the key is found, you should remove the malicious files and background programs using Cursor's official remediation scripts. Furthermore, you should also change passwords, access keys and other login details from a trusted, unaffected device.
Cursor has also warned that simply uninstalling the extension may not be enough, as harmful background programs could continue running.