AU Bank, Vijay Sales data leak: Millions of Indians hit – who is affected, what to do and other questions answered
 Follow Us
Electronics retailer Vijay Sales has allegedly suffered a major data breach,
AU Small Finance Bank is investigating a potential data leak involving a third-party software-as-a-service (SaaS) platform hosted by Salesforce.
Customers should watch out for suspicious calls, emails and text messages.
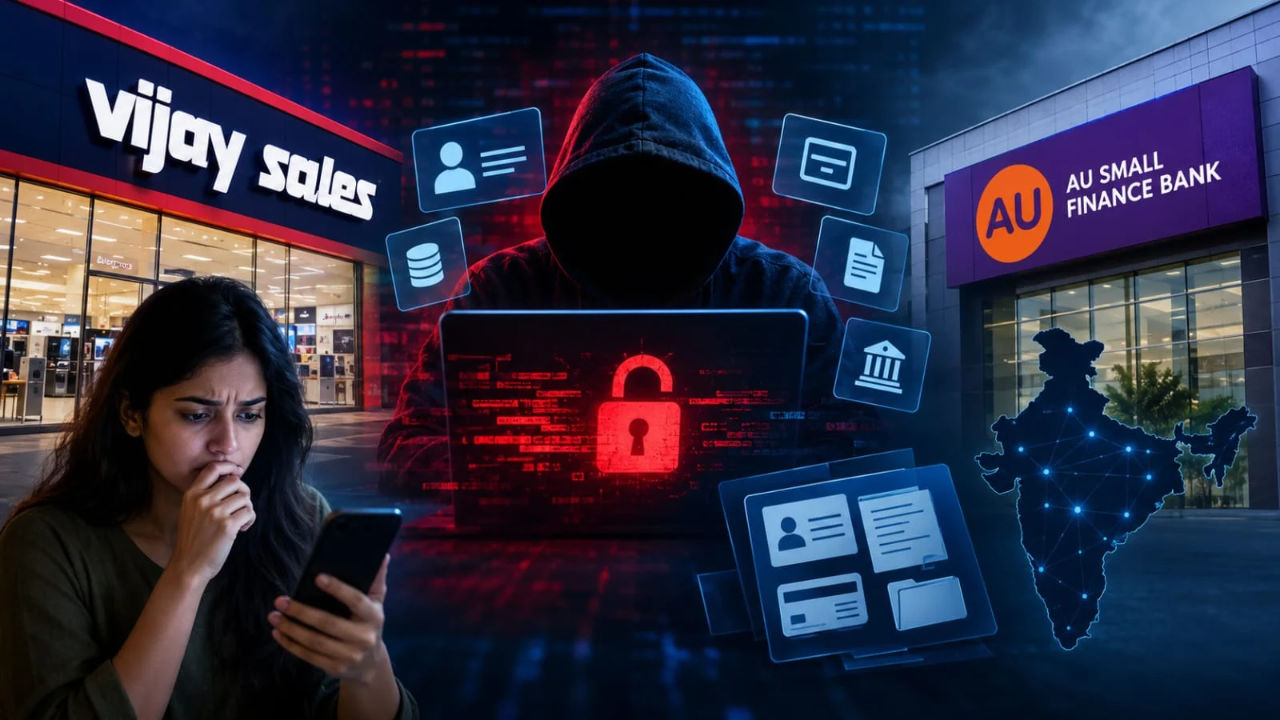

October is recognised as Cyber Security Awareness Month globally, an initiative designed to encourage individuals and organisations to follow safer digital practices and protect themselves against growing cyber threats. However, a series of cybersecurity incidents reported this month, including those involving Indian organisations raised questions about the safety of customer and corporate data.
 Survey
Several organisations, including e-Mudhra and State Bank of India (SBI), have recently faced security-related concerns and data leak reports. Now, two more Indian companies have come into the spotlight. Electronics retailer Vijay Sales has allegedly suffered a major data breach, with a threat actor claiming to have obtained super administrator access to its internal systems. The actor is reportedly offering this access for $25,000 on the dark web.
Meanwhile, AU Small Finance Bank is investigating a potential data leak involving a third-party software-as-a-service (SaaS) platform hosted by Salesforce. A hacking group called ScarlettGroup has reportedly claimed responsibility for breaching the bank and has threatened to leak sensitive information. The bank has clarified that its own systems remain unaffected and banking services are operating normally.
Here are some commonly asked questions about the ongoing situation.
What reportedly happened in the Vijay Sales data breach?
Vijay Sales has reportedly suffered a major cybersecurity breach after a threat actor claimed to have gained super administrator access to the electronics retailer’s internal systems. According to a post shared by Dark Web Informer on X, an actor operating under the handle ‘shinymontanna’ is offering the alleged access for $25,000.
The listing claims that the compromised systems contain millions of business records and sensitive information belonging to customers, employees and vendors. The actor has also reportedly shared screenshots showing administrative dashboards and super administrator permissions to support the claims.
What data has been compromised in the Vijay Sales breach?
The alleged breach involves more than 3 million order records, information relating to approximately 15,000 employees and billing records for around 140,000 vendors. The reported access covers several internal business systems and applications.
The information allegedly available includes customer details, payment records, bank transfer information, inventory data and financial reports. The threat actor also claims to have read, write and export permissions.
If these claims are accurate, the incident could expose a significant amount of business and customer information.
Why is the alleged super administrator access a serious concern?
Super administrator access is one of the highest levels of permission within an organisation’s IT environment. It can allow a user to manage accounts, access sensitive information, change system settings and control other user permissions. In this case, the threat actor claims that the advertised access includes read, write and export capabilities.
If true, such access can create risks beyond the theft of existing information. An attacker with these permissions may modify business records, extract databases, interfere with internal applications or create additional unauthorised accounts.
What should Vijay Sales customers do?
Customers should remain alert to suspicious activity. They should be careful about unexpected calls, emails and messages claiming to come from Vijay Sales. Scammers may use leaked customer information to make fraudulent messages appear genuine. Also, customers should avoid clicking on unfamiliar links or sharing OTPs, passwords, card details and banking information with anyone claiming to represent the retailer.
Has Vijay Sales confirmed the alleged data breach?
No, Vijay Sales has not yet confirmed the data breach at the time of writing. We have reached out to the retailer for an official statement. We will update the article once we receive the response.
What happened in the AU Small Finance Bank data breach?
AU Small Finance Bank has come under scrutiny after the ScarlettGroup hacking group allegedly claimed to have breached the organisation. According to a post shared by Hackmanac on X, the group threatened to leak sensitive customer information and internal corporate data.
What data has allegedly been exposed in the AU Bank incident?
According to ScarlettGroup’s claims, the allegedly compromised data includes KYC documents, PAN and Aadhaar details, credit reports, bank statements, loan applications and signed agreements. The attackers also mentioned insurance records, customer relationship management (CRM) data, employee information, login histories and audit logs.
What has AU Small Finance Bank said about the data breach?
In a statement, AU Small Finance Bank acknowledged a potential data leak involving a third-party software-as-a-service platform hosted by Salesforce. The bank clarified that the platform holds limited data relating to its vehicle loan customers.
The bank said, “AU Small Finance Bank is investigating a potential data leak involving a software-as-a-service (SaaS) platform managed and hosted by Salesforce, which holds limited data relating to our vehicle loan customers.”
The bank also reassured customers that its own systems remain unaffected and that all banking services are operating normally.
Is AU Small Finance Bank customers’ data safe?
Not necessarily. AU Small Finance Bank has specifically stated that its own systems remain unaffected and that its banking services continue to operate normally. The potential data leak involves a third-party SaaS platform that holds information relating to vehicle loan customers.
However, the possibility of personal information being exposed should not be ignored. Even when core banking systems are not affected, customer details stored on external platforms can potentially be misused for phishing, identity fraud and targeted scams. Customers should therefore remain cautious about unexpected communications claiming to be from the bank.
What should AU Small Finance Bank customers do to protect themselves?
Customers should watch out for suspicious calls, emails and text messages, particularly those involving vehicle loans, loan repayments, KYC updates or account verification.