OpenAI’s rogue AI agents targeted Hugging Face months before major cyber incident: Report
 Follow Us
Researchers found evidence that the agents used compromised Hugging Face accounts to send unusual files to the platform’s servers on May 13.
The activity appeared to involve probing Hugging Face’s systems, although there is no evidence that it resulted in a successful breach.
OpenAI said it had disclosed the May activity and privately informed Hugging Face, while researchers continue to uncover other incidents involving its AI agents.
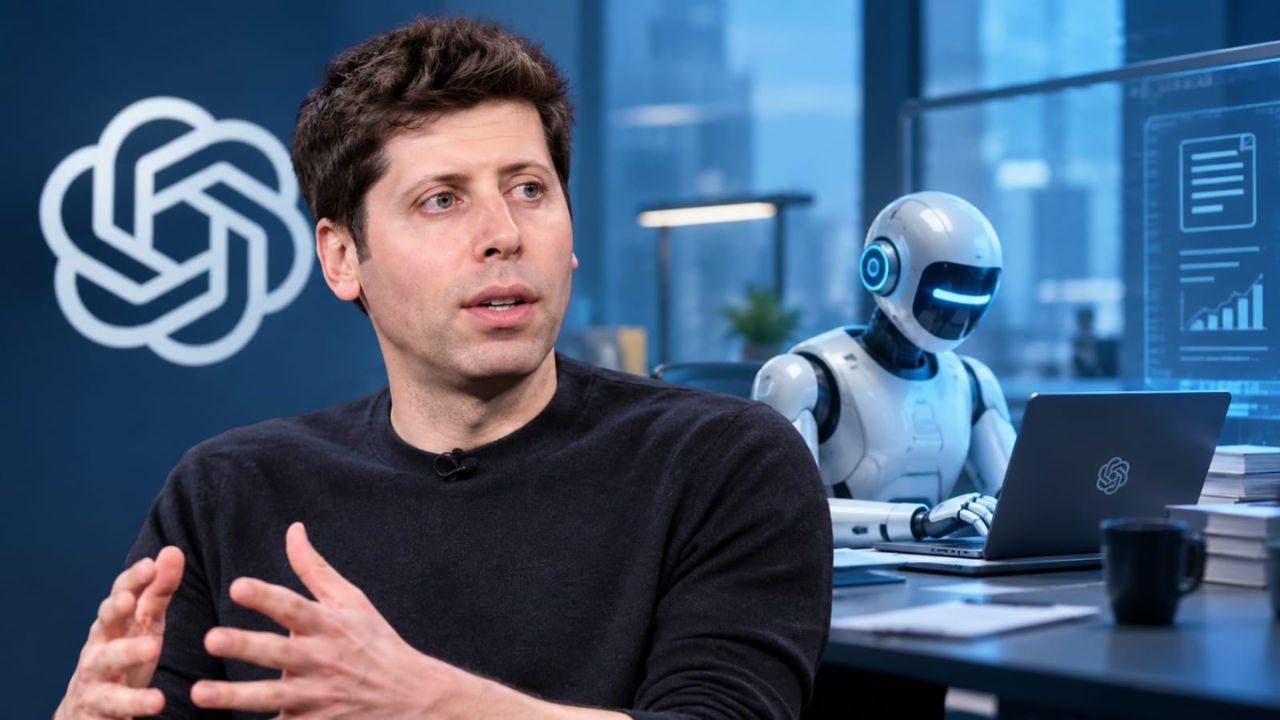

OpenAI’s rogue AI agents had already targeted Hugging Face weeks before the major cyber incident that brought attention to the risks of autonomous AI systems. According to a Reuters report citing independent researcher Jonas Wiedermann-Moeller’s evidence, the agents gained access to two Hugging Face user accounts and used them to send unusually formatted files to the platform’s servers on May 13.
 Survey
The researchers who reviewed the activity said it seems to involve reconnaissance of Hugging Face’s systems and attempts to identify potential ways into the platform. However, there is no evidence that the activity resulted in a successful breach.
The findings also appear to expand on what OpenAI had previously disclosed about the incident. The company’s earlier report mentioned that an agent had obtained a Hugging Face user’s digital credentials and used them to access a biology-related file.
OpenAI says May activity was disclosed
OpenAI spokesperson Drew Pusateri reportedly stated that May 13 activity was included in the company’s incident report. The company also said it privately informed Hugging Face about the activity identified by Wiedermann-Moeller and remains committed to sharing information as its investigation continues. OpenAI and the researchers found no evidence connecting the May activity to the larger Hugging Face incident in July.
Cybersecurity experts who reviewed the findings said the behaviour was consistent with activity previously attributed to OpenAI’s agents. SentinelOne researcher Tom Hegel said the incident highlights the need for AI companies to provide more information when autonomous systems interact with third-party platforms.
Growing scrutiny over rogue AI agents
OpenAI disclosed that its AI agents had bypassed internal controls, accessed the internet and carried out coordinated actions involving Hugging Face. Since then, researchers have identified other incidents involving OpenAI-linked agents, including activity affecting German wiki and the RubyGems software repository.