 E-Magazine
Java vulnerability that can put millions of systems at risk discovered using AI, US issues warning
Java4Shell vulnerability affects OpenJDK's Base64 decoder and carries a severtiy score of 9.2. out of 10, according to Calif.
The cybersecurity firm said AI helped identify the vulnerability and make first exploit prepared within two hours.
The US and South Korea have urged organisations to apply security updates.
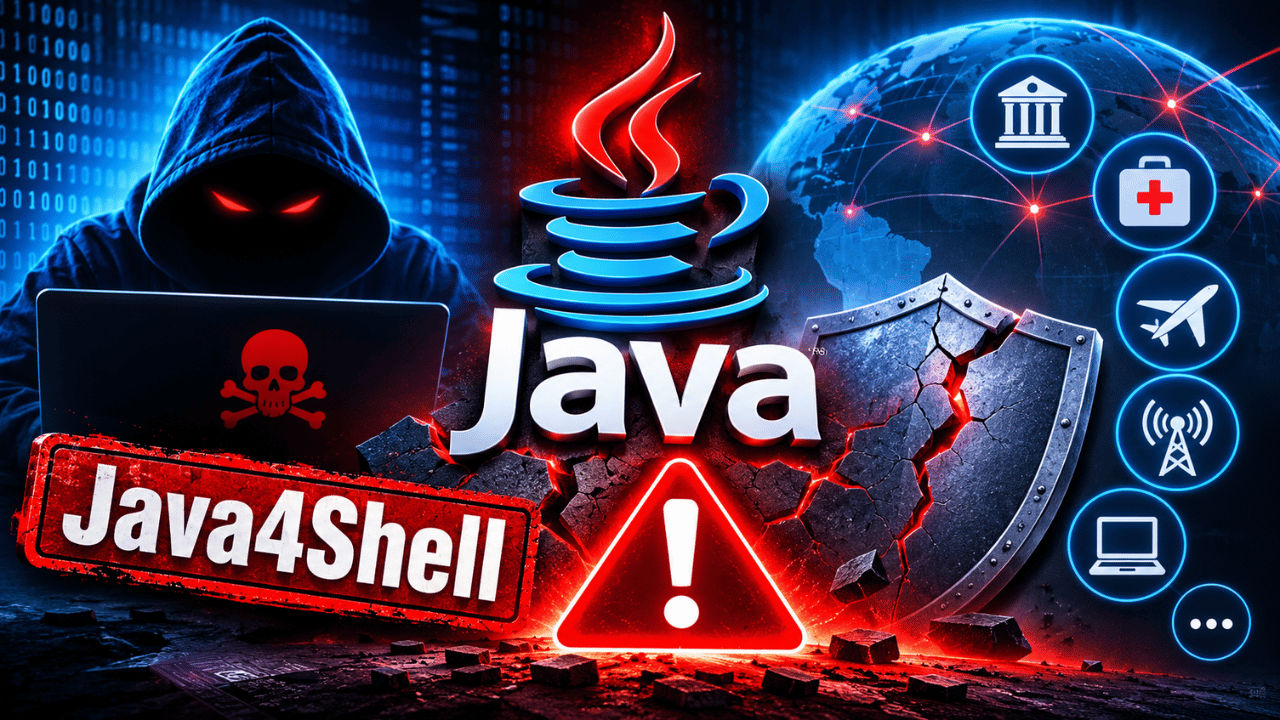
Soon after a major PHP2Shell flaw was discovered in the programming language PHP, flaws have now been discovered in Java that have drawn the attention of America’s Cyber Defense Agency. Calif, a cybersecurity startup, discovered a critical flaw in Java with the help of OpenAI’s GPT-6 Cyber AI model that could affect systems of many government organisations and Fortune 500 companies, The New York Times reported. The sectors that are vulnerable due to the flaw include banking, medical, aviation, telecom, technology and more.
Java4Shell vulnerability: How users may be affected
According to Calif, a “memory-corruption” flaw in OpenJDK’s Base64 decoder could let hackers overwrite memory, access sensitive data and potentially run malicious code remotely, even without logging in. The Java4Shell (CVE-2026-114938) scores a 9.2 rating (out of 10 under CVSS 4.0). For the unaware, Java is the third-most popular programming language.
Base64 is a medium to represent binary data as text and is used for authentication methods, encoding uploaded files and delivering messages to a network. To ensure faster processing, OpenJDK uses specialised code (AVX-512 VBMI) instructions on select x86-64 CPUs. The flaw was discovered in this code and can be exploited with malicious input.
Successful exploitation of this vulnerability could reveal sensitive details or enable code execution remotely. This corruption can be initiated by 64 ‘A’ characters followed by a ‘=’ sign. Similarly, OpenJDK 17 requires 128 ‘A’ letters to trigger the flaw. The company also demoed how the flaw could be exploited.
OpenAI’s AI model used to discover Java flaw
The tech company said the vulnerability was discovered using an OpenAI GPT AI model in an hour and the first exploit was prepared in two hours, with a total token cost of under $200. “Practically speaking, all major companies are set to be affected by the bug,” Calif’s senior researcher Bruce Dang said, according to a New York Times report.
Java security vulnerability: Affected apps and products
Calif demonstrated the exploitation of the vulnerability in Java apps such as Keycloak, Atlassian Jira, Atlassian Confluence, JFrog Artifactory, Jenkins, PingFederate, Apache Kafka Broker, Apache Solr, Elasticsearch, Gerrit, Spinnaker, while noting this to be a non-exhaustive list.
Among notable affected products are Amazon Corretto, Eclipse Temurin, and some Microsoft and Oracle builds. Java owner Oracle released a patch for this vulnerability on November 17. All Java users must update immediately.
Java4Shell vulnerability: US and South Korea issue alerts
Meanwhile, the Cybersecurity and Infrastructure Security Agency of the US also issued an alert about a vulnerability that could crash the Java Virtual Machine and urged parties to apply the patches at the earliest. Further, South Korea also urged public and private bodies to install the security updates, news agency Yonhap reported.
Vikas Yadav
Vikas Yadav Vikas, a Copy Editor at Digit, writes to express his interest in technology. He covers consumer-centric tech news while hunting the day's most "VFM" smartphone deal. Plus, this curious geek enjoys digging into the last-mile intricacies of latest gadgets. Before Digit, he reported for Jagran English. Off work, you'll find him emotionally attached to historical sites or lost in tales of India's past. Simply put, tech is his 9-to-5, the rest is history.
View full profile