Beware iPhone users! This new DarkSword spyware can steal your passwords and other info, how to protect your data
 Follow Us
P7 DarkSword spyware can target saved passwords, private notes and crypto wallet data.
The malware can hide its activity and steal iPhone data by following remote instructions.
Users should update to the latest iOS version and avoid suspicious websites to stay safe.
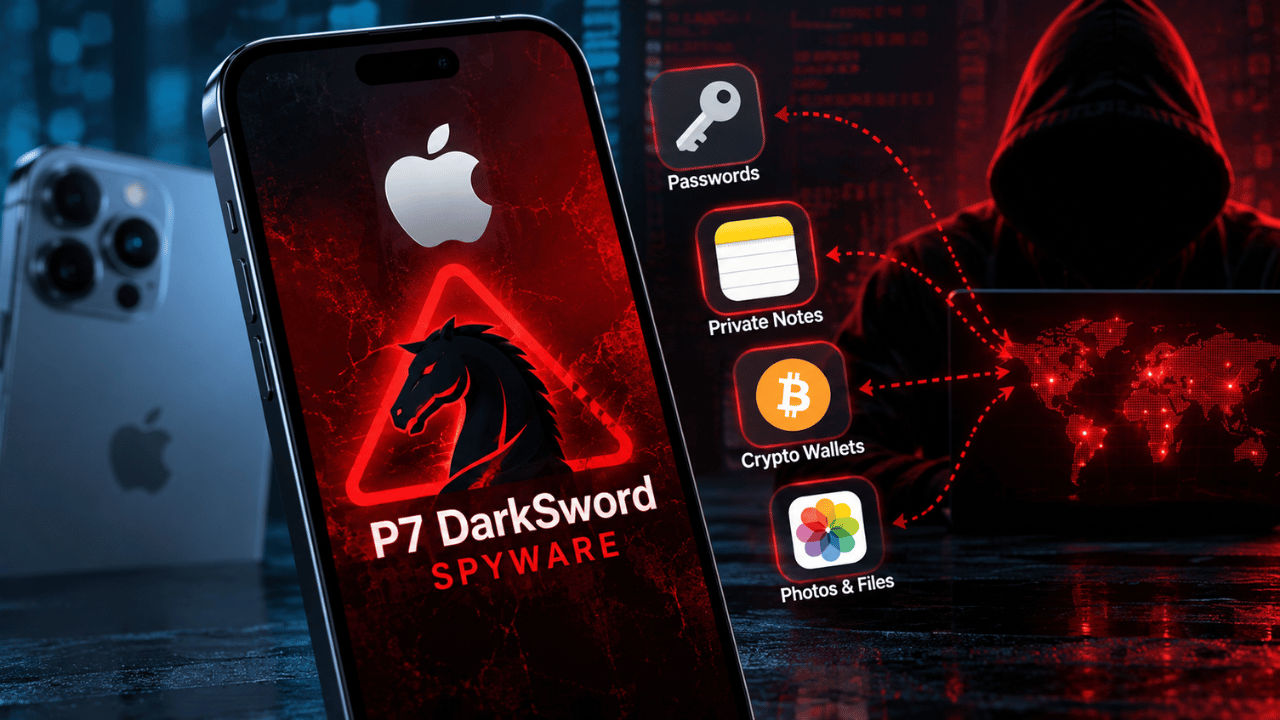

Apple is known for its security and data safety, but a new DarkSword malware is said to be targeting sensitive data. According to the latest report, the new version of the malware can process saved Keychain information directly on the device and can target cryptocurrency wallet data and communicate with attackers for further instructions. Aside from that, your saved passwords and private notes can also get targeted. The malware also reduces some of its activities to stay hidden from the security teams. Here is what the report says about the new P7 DarkSword malware and how it can affect your iPhone.
 Survey
P7 DarkSword malware: What is it?
iVerify named the new DarkSword malware P7 DarkSword because of the changes made to the original malware’s code. According to them, the new variant focuses on three areas, which are staying hidden, avoiding repeated attacks on the same device and stealing more data.
Not only that, but the threat-hunting platform also noted that the new version of the malware reduces activity that could reveal its presence and uses browser storage to help prevent the same iPhone from being exploited repeatedly. Furthermore, unlike earlier versions, it can also process keychain data directly on the device before sending it to attackers.
P7 DarkSword malware: How it steals iPhone data
The report suggests that the malware communicates with a remote server controlled by attackers and checks for new instructions every 15 seconds by default. It also pointed out that the interval can be changed by the attackers to their liking.
It’s also reported that once instructed, the malware can upload photos, list installed apps, collect files and copy Apple Notes databases. Moreover, it can also scan the device’s storage and target information linked to certain cryptocurrency wallets.
Also read: Tim Cook says he is not meddling in John Ternus’s work, reveals his advice to new Apple CEO
How iPhone users can stay safe
DarkSword is an exploit-based hacking tool and was previously linked to attacks against iPhones running older versions of iOS, especially users running on iOS 18.4 to iOS 18.7. While Apple has not officially said anything about it at the time of writing, iVerify said that users should install the latest iOS updates available for their devices to stay protected against the malware. Not only that, but they also advised users to avoid suspicious websites and never assume that malicious web content is safe simply because it appears on a familiar page.