Meta pauses Muse AI feature after researchers uncover exposed business secrets
 Follow Us
Claroc found 6,800+ share-related hostnames but inspected only a few hundred pages.
Examples included a CEO’s revenue review, a loan application and a bank fraud alert.
No misuse found, and rechecked links no longer open, though DNS records retain some titles.
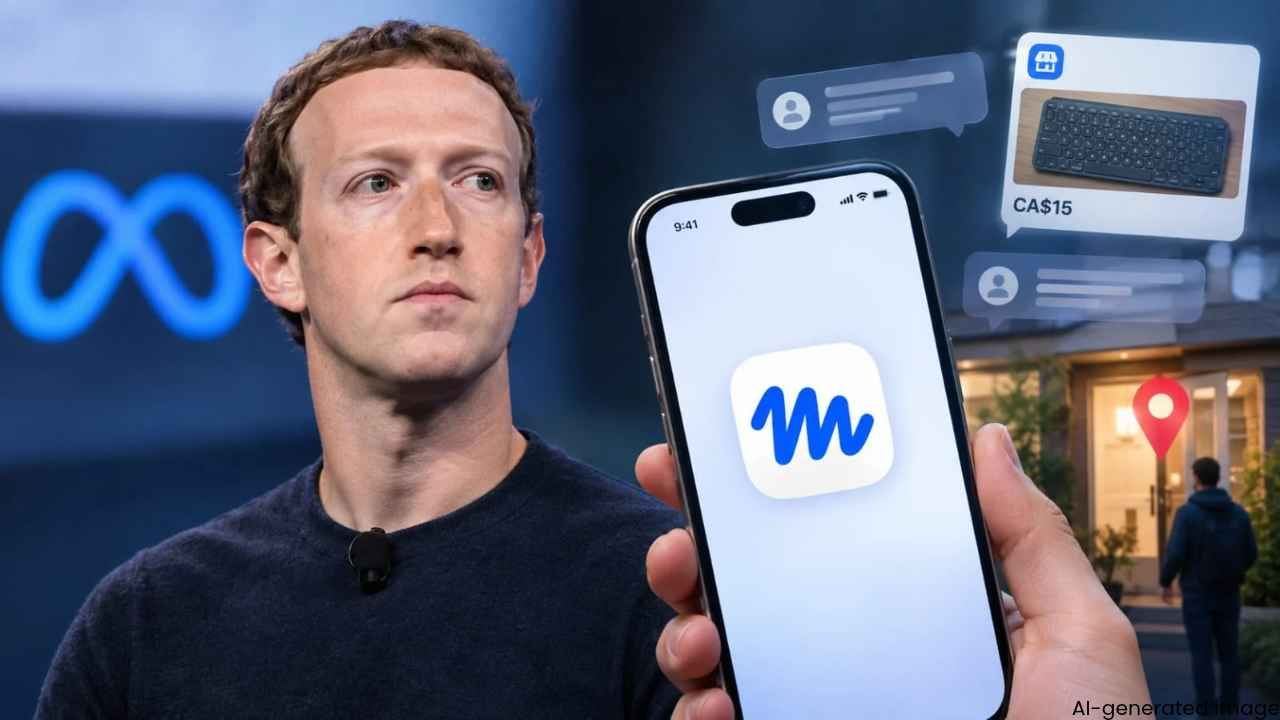

Meta has paused a conversation sharing feature in its Muse AI assistant after researchers discovered a privacy flaw that may have exposed confidential business information. The issue affected conversations that users had chosen to share, rather than all private chats on the platform. This comes after researchers at Claroc reported the vulnerability to Meta through its bug bounty programme on October 8, 2026.
 Survey
As per Claroc, shared conversations were hosted on Meta AI subdomains. Researchers found that these links can potentially be discovered through passive DNS records and scans saved on the public website urlscan.io. Some records included readable conversation titles alongside random identifiers, making it possible to identify potentially sensitive discussions.
It identified over 6,800 share-related hostnames after filtering out unrelated DNS records. However, researchers inspected only a few hundred pages, and the findings do not establish that all these links exposed sensitive information.
Also read: Microsoft Xbox eyes 3 rounds of fresh layoffs, to launch Xbox handheld next year: Report
The researchers during their investigation were able to find a few things including a marketing company’s revenue review prepared for its CEO, a small-business loan application, a property investor’s financial report and a bank fraud alert containing partial account details. Other examples included a staff vacation calendar and confidential preparations for an executive search call involving an AI laboratory. The researchers said they found no evidence that the exposed information had been misused. They also withheld identifying details about the affected individuals and businesses.
Even when people intentionally share a chat, they often don’t realize that connected links and background details can easily end up exposed on third-party sites. Claroc also noted that a crawler restriction in Meta AI’s robots.txt file did not prevent people from accessing the pages or stop passive DNS services from recording hostnames.
After Meta paused the feature, researchers revisited 40 previously accessible links and found that none opened. The associated content-hosting addresses also returned errors, although historical DNS records continued to retain some hostnames and titles. It must be noted that Meta has not publicly confirmed the full extent of the exposure.