Google, Apple and Mozilla block eMudhra certificates after researchers uncover critical security flaw: How to be safe?
 Follow Us
The affected keys could be recovered by testing just 256 possible values, exposing a serious cryptographic flaw.
Google, Apple and Mozilla have blocked the affected certificates and introduced protections for their users.
eMudhra blamed a script error during certificate generation, with no evidence so far that the compromised keys were used maliciously.
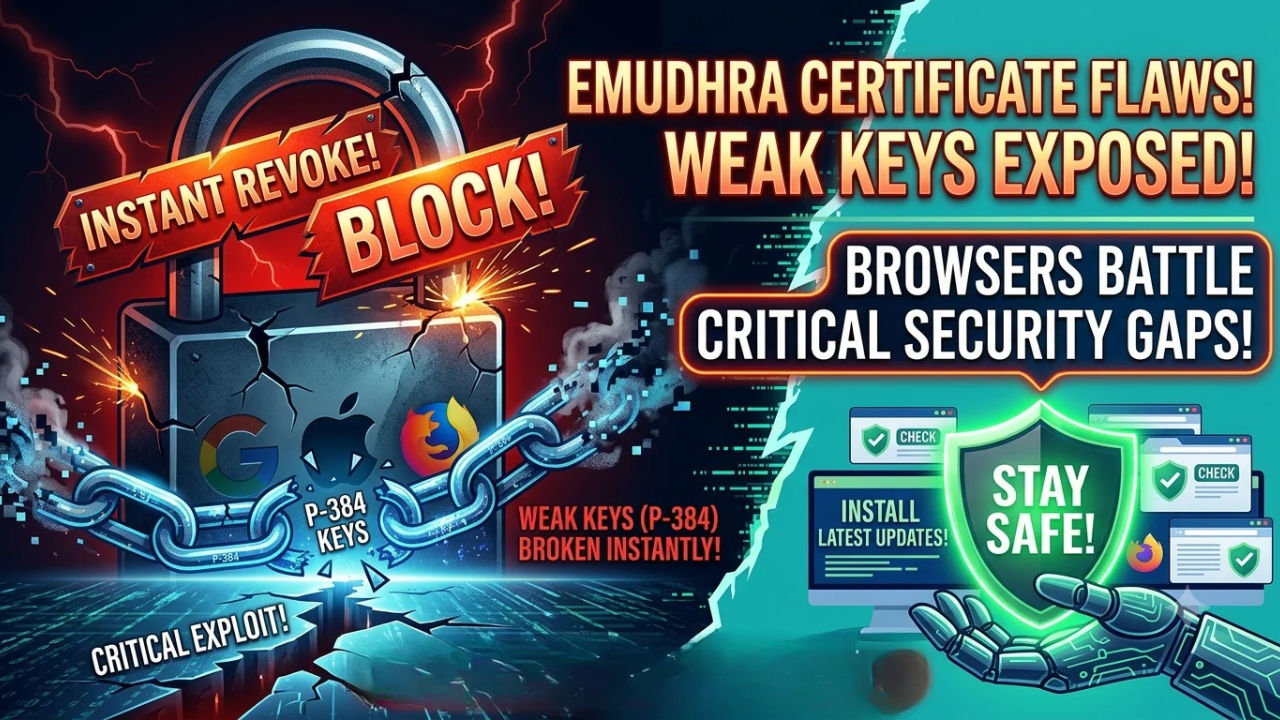

Indian certificate authority eMudhra has revoked eight intermediate digital certificates after security researchers discovered that their private keys were so weak they can be recovered instantly. The flaw might have allowed attackers to create trusted certificates for legitimate websites. In simple terms, this means the threat actors can impersonate websites and intercept encrypted communications more easily than you think.
 Survey
The vulnerability was discovered on October 17 by a security researcher known as Wayne, who was examining publicly available certificate data. Mozilla’s incident report revealed that the affected certificates used P-384 cryptographic keys generated in April 2025. However, the keys contained values smaller than 256, meaning an attacker could recover them by testing just 256 possibilities.
Security researcher Flüpke demonstrated the problem by publishing one of the compromised private keys on GitHub. The key associated with eMudhra’s EM OV TLS CA – G3C certificate had a value of just four, a report cited.
How the eMudhra certificate flaw occurred
In its response to Mozilla, eMudhra attributed the incident to an error in a certificate-generation script used in April 2025. The mistake reportedly produced a second set of cryptographic keys with weaker values. These were subsequently selected for certificate signing because their labels resembled those of correctly generated keys.
Some affected certificates were also submitted to Sectigo for cross-signing. Although eMudhra said most of the certificates had not been used in production and that it had found no evidence of end-user certificates being issued through them, the weak keys could potentially have been exploited since their creation.
There is currently no evidence that attackers used the compromised keys to issue malicious certificates.
Browsers and software providers roll out fixes
After the disclosure, eMudhra revoked all eight certificates and halted new certificate issuance under its G3 root.
Mozilla blocked the affected certificates through Firefox’s OneCRL system on October 17. Google Chrome also blocked six compromised intermediates authorised to issue TLS certificates, while Apple introduced protections on October 19.
Security experts warn that identifying and updating every affected system could take considerable time, particularly for older servers, embedded devices and internet-connected appliances.
Users should install available browser, operating system and application updates. While major browser vendors have already implemented protections, systems relying on outdated certificate stores may remain vulnerable until their software is patched.